Understanding 21 CFR Part 11 and FDA Electronic Signature Rules
The U.S. Food and Drug Administration’s (FDA) 21 CFR Part 11, enacted in August 1997, stands as a critical regulation governing the use of electronic records and electronic signatures within FDA-regulated industries. This includes pharmaceuticals, biologics, and medical devices. Its core purpose is to ensure that electronic records and signatures are considered trustworthy, reliable, and legally equivalent to paper records and handwritten signatures. In October 2026, over two decades since its inception, Part 11 remains highly relevant, serving as the foundation for data integrity in GxP environments.
The scope of Part 11 is broad, applying to all electronic records that are created, modified, maintained, archived, retrieved, or transmitted under the regulatory authority of the FDA. This encompasses records mandated by predicate rules (e.g., Good Manufacturing Practices (GMP), Good Clinical Practices (GCP), Good Laboratory Practices (GLP)) when they are kept in electronic form instead of paper, or when they are submitted to the FDA electronically. The regulation aims to guarantee the authenticity, integrity, and confidentiality of electronic data, protecting public health.
Core Requirements: Dual-Component Authentication and Record Linking
At the heart of Part 11’s requirements for electronic signatures is the principle of non-repudiation – ensuring that a signer cannot falsely deny having signed a document. To achieve this, the FDA mandates specific controls.
Firstly, electronic signatures must be uniquely assigned to an individual and their identity must be verified before the signature is established. This is a foundational step, ensuring accountability. Secondly, as per § 11.200, non-biometric electronic signatures require a multi-component authentication process. This typically involves at least two distinct identification components, such as a user ID and a password. For the initial signing action within a continuous, controlled access session, all components must be used. For subsequent signings within that same session, at least one component unique to the individual is required. Biometric signatures, which rely on unique physiological characteristics, also have stringent safeguards to prevent unauthorized use.
Furthermore, § 11.50 dictates that when an electronic signature is applied, its “manifestation” must clearly display specific information alongside the signed electronic record. This includes the printed name of the signer, the date and time of the execution, and the meaning associated with the signature (ee.g., review, approval, authorship, responsibility). This transparency is crucial for traceability and understanding the context of the signature.
Most importantly, § 11.70 mandates that electronic signatures must be securely linked to their respective electronic records. This linkage must be robust enough to prevent the signature from being excised, copied, or otherwise transferred to falsify a record. This ensures the integrity of the signed document, making the electronic signature an integral part of the record itself. Before an organization can even begin using electronic signatures in FDA-regulated systems, they must submit a formal, handwritten certification to the FDA, confirming their intent for electronic signatures to be legally binding equivalents of handwritten ones.
Closed Systems vs. Open Systems Under Part 11
21 CFR Part 11 distinguishes between two types of electronic systems, each with specific control requirements based on their accessibility and security needs. Understanding this difference is crucial for implementing appropriate safeguards.
Closed Systems are defined as environments where system access is controlled by persons who are responsible for the content of electronic records that are on the system. These systems typically operate within an organization’s internal network, under its direct control.
Open Systems, conversely, are environments where system access is not controlled by persons who are responsible for the content of electronic records that are on the system. This often refers to systems accessible over public networks, such as the internet, where data transmission occurs outside the organization’s immediate control.
The distinction necessitates different technical controls, with open systems requiring additional measures to protect data integrity and authenticity.
Feature/Control Closed System (§ 11.10) Open System (§ 11.30) Access Control Limited to authorized personnel Limited to authorized personnel System Validation Required for accuracy, reliability, consistent performance Required for accuracy, reliability, consistent performance Audit Trails Secure, computer-generated, time-stamped Secure, computer-generated, time-stamped Operational Sequencing Required for proper order of manual steps Required for proper order of manual steps Authority Checks Prevent unauthorized system access/operations Prevent unauthorized system access/operations Record Copies Accurate and complete copies for inspection Accurate and complete copies for inspection Protection from Falsification Technical and procedural controls Technical and procedural controls plus encryption Electronic Signature Security Unique, multi-component authentication Unique, multi-component authentication plus digital signature standards Data Integrity Maintained through system controls Maintained through system controls and encryption For closed systems (§ 11.10), controls primarily focus on robust system validation, secure audit trails, access limitations, operational sequencing, and authority checks. These measures are designed to ensure data integrity within a controlled environment.
For open systems (§ 11.30), all the controls required for closed systems apply, but with the crucial addition of measures to protect records during transmission over uncontrolled networks. This includes the use of document encryption and adherence to digital signature standards, such as those based on Public Key Infrastructure (PKI), to ensure the authenticity and integrity of records and signatures from their point of creation to their destination. This layered security is vital to prevent unauthorized access, alteration, or repudiation in less secure environments.
How Predicate Rules Govern Electronic Records
While 21 CFR Part 11 provides the overarching framework for the trustworthiness of electronic records and signatures, understand that it does not create new record-keeping requirements. Instead, Part 11 layers upon existing “predicate rules.” These predicate rules are the specific FDA regulations (e.g., 21 CFR Part 211 for GMP, 21 CFR Part 58 for GLP, 21 CFR Part 312 for GCP, and international guidelines like ICH E6) that mandate what records must be kept and how they should be managed, regardless of whether they are paper or electronic.
The interaction is symbiotic: predicate rules define the content and purpose of a record (e.g., a batch record, a clinical trial protocol, a laboratory notebook entry), while Part 11 dictates the technical and procedural controls necessary to ensure that an electronic version of that record, and any associated electronic signatures, are as reliable and legally binding as their paper counterparts.
For instance, a pharmaceutical company’s electronic batch records, which detail the manufacturing process, must comply with 21 CFR Part 211 (cGMP). If these records are maintained electronically, then Part 11’s requirements for validation, audit trails, and electronic signatures come into play. Similarly, in clinical research, an electronic Trial Master File (eTMF) must adhere to GCP guidelines (like ICH E6). Any electronic signatures used for approvals or reviews within the eTMF must then meet Part 11’s criteria for authenticity and integrity.
The FDA’s 2003 guidance on Part 11 clarified that the agency would exercise enforcement discretion, focusing on predicate rule compliance. This means that if an electronic record is not required by a predicate rule, or if it is merely a copy of a paper record, it may not be subject to all Part 11 controls. However, for records used in lieu of paper or submitted to the FDA, full Part 11 compliance is expected. Therefore, organizations must carefully evaluate their record-keeping practices against both predicate rules and Part 11 to determine the appropriate validation scope and control implementation. This often involves integrating Part 11-compliant features directly into systems like Laboratory Information Management Systems (LIMS) or Electronic Document Management Systems (EDMS) to streamline compliance.
Modernizing GxP Compliance with a Digital Validation Platform
The traditional approach to GxP compliance, particularly for computer system validation (CSV), has often been characterized by manual, document-heavy processes. However, as technology evolves and regulatory expectations mature, organizations are increasingly seeking more efficient, reliable, and agile methods. This shift is driving the adoption of digital validation platforms, aligning with modern methodologies like Computer Software Assurance (CSA) and the GAMP 5 framework. These platforms enable organizations to transition from reactive, paper-based validation to proactive, automated, and continuous compliance.
By leveraging automated workflows, digital validation platforms significantly reduce the time and resources traditionally consumed by CSV. They embed data integrity principles directly into the system lifecycle, ensuring that electronic records and signatures are inherently trustworthy from design to retirement. This modernized approach embraces a risk-based validation strategy, focusing critical testing efforts on areas that directly impact patient safety, product quality, and data integrity, rather than on exhaustive, non-value-adding documentation.
Why Traditional Paper and Spreadsheet Validation Fail
For decades, many organizations relied on manual processes, paper documentation, and even spreadsheets for managing critical GxP data and validation activities. While seemingly cost-effective initially, these traditional methods are fraught with vulnerabilities that often lead to compliance failures and significant risks.
Spreadsheets, for instance, are notoriously difficult to control in a Part 11 compliant manner. They inherently lack robust built-in version control, making it challenging to track changes and revert to previous states. Audit trail capabilities are either non-existent or easily circumvented, failing to capture who made what changes, when, and why. This absence of granular control opens the door to manual errors, unauthorized alterations, and even deliberate data falsification, undermining the authenticity and integrity of electronic records.
The consequences of such failures can be severe. FDA inspections frequently uncover deficiencies related to inadequate data integrity controls, leading to FDA Form 483 observations and, in serious cases, Warning Letters. These enforcement actions can result in costly remediation efforts, production delays, damage to reputation, and even product recalls. In an era where electronic records are paramount, relying on outdated validation and data management practices is not just inefficient; it’s a significant regulatory and business risk.
Core Capabilities of an AI-Powered Digital Validation Platform
To overcome the inherent limitations of traditional methods, organizations are turning to advanced solutions that embed compliance directly into their digital ecosystem. An AI-powered digital validation platform represents a paradigm shift, offering a comprehensive suite of capabilities designed to streamline and strengthen GxP compliance.
These platforms leverage artificial intelligence and automation to transform the entire validation lifecycle. Key capabilities include automated testing, which can execute predefined test scripts across various systems, significantly reducing manual effort and human error. Risk assessment is dynamically integrated, allowing for continuous evaluation of system components and focusing validation efforts where they are most needed. The platform automates the generation of essential validation documentation, including Installation Qualification (IQ), Operational Qualification (OQ), and Performance Qualification (PQ protocols and reports, ensuring consistency and completeness.
Perhaps one of the most powerful features is dynamic traceability. This capability ensures that every requirement, risk, test case, and defect is linked throughout the system lifecycle, providing a clear, auditable trail. This not only simplifies audits but also ensures that changes are managed effectively and their impact fully understood. By automating these complex processes, an AI-powered validation solution drastically reduces the time and cost associated with compliance, while simultaneously enhancing data integrity and reliability. Organizations looking to future-proof their GxP operations and ensure robust electronic signature compliance should explore how a modern digital validation platform can transform their approach.
Technical Controls: Audit Trails, Encryption, and Access Security
Implementing robust technical controls is non-negotiable for achieving and maintaining FDA electronic signature compliance. These controls form the backbone of data integrity and security for electronic records.
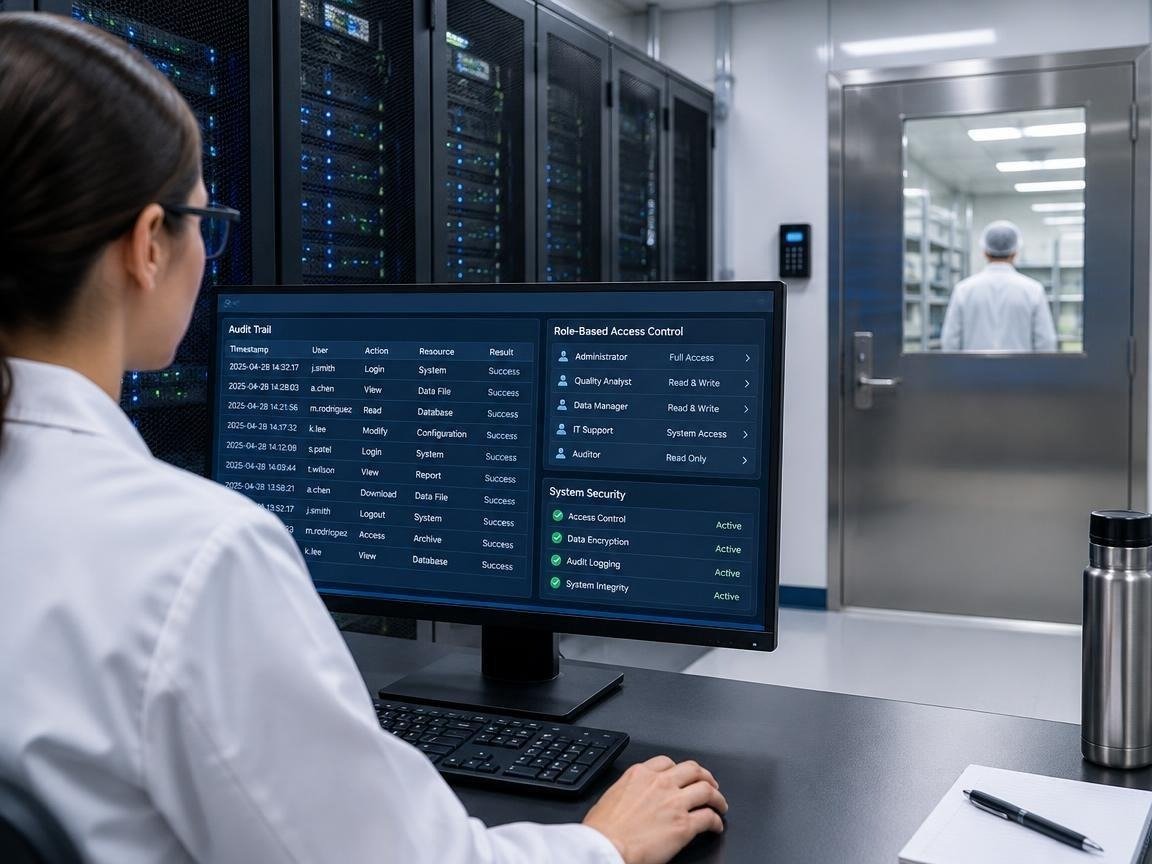
Audit Trails: Part 11 mandates secure, computer-generated, time-stamped audit trails. These logs must independently record the date and time of operator entries and actions that create, modify, or delete electronic records. Crucially, they must not obscure any previously recorded information. An immutable audit trail provides a comprehensive history of all changes, identifying who made them, when, and the reason for the change. This capability is vital for demonstrating accountability and detecting any unauthorized alterations.
Encryption: For open systems, and as a best practice for closed systems, encryption is paramount. This involves protecting data both at rest (when stored) and in transit (when being transmitted). Data-at-rest encryption safeguards stored electronic records from unauthorized access, even if the storage medium is compromised. Data-in-transit encryption protects records and electronic signatures as they move across networks, especially public ones, ensuring their confidentiality and integrity.
Access Control: Limiting system access to authorized personnel is a fundamental control. This is achieved through robust authentication mechanisms, such as multi-factor authentication (MFA), which requires users to provide two or more verification factors to gain access. Role-based access controls (RBAC) further refine this by granting users only the permissions necessary for their specific job functions, preventing unauthorized actions. Additionally, policies for password aging, periodic revisions, and immediate deauthorization of compromised credentials are essential to maintain security. These layered controls collectively ensure that only authenticated and authorized individuals can interact with critical electronic records and apply electronic signatures.
Overcoming Implementation Challenges and FDA Inspection Risks
Implementing and maintaining 21 CFR Part 11 compliance presents ongoing challenges for regulated entities. The dynamic nature of technology, coupled with evolving regulatory interpretations, means that compliance is not a one-time event but a continuous process. Organizations must prioritize inspection readiness, proactively mitigate risks, and embed quality management principles throughout their electronic systems lifecycle. Staying abreast of FDA enforcement trends and investing in sustainable compliance strategies are crucial for long-term success.
Mitigating Common Audit Findings and Non-Compliance Pitfalls
FDA inspections often uncover recurring issues related to electronic records and signatures, leading to significant audit findings and potential enforcement actions. Common pitfalls include:
- Unlinked Signatures: Electronic signatures not properly linked to their corresponding records, making it impossible to verify their authenticity or context.
- Shared Credentials: The practice of multiple individuals using the same user ID and password, which completely undermines the unique assignment requirement of Part 11 and destroys accountability.
- Missing Change Reasons: Audit trails that record changes but fail to capture the reason for the modification, making it difficult to understand the intent behind the action.
- Inadequate Legacy System Handling: Failure to properly assess and document legacy systems (those operational before August 20, 1997) and ensure their continued predicate rule compliance, even if they are exempt from some Part 11 technical controls.
- Lack of SOP Enforcement: Having written Standard Operating Procedures (SOPs) for electronic record and signature use, but failing to ensure staff adherence or proper training.
To mitigate these risks, organizations must conduct regular internal audits, enforce strict policies against shared credentials, and ensure that all electronic signature workflows capture the required metadata, including the meaning of the signature. The FDA’s enforcement discretion for legacy systems, as outlined in their 2003 guidance, requires documented justification that these systems continue to meet predicate rule requirements. A robust quality management system that supports continuous training and rigorous SOP enforcement is key to avoiding these common non-compliance issues.
Accelerating CSA and System Lifecycle with a Digital Validation Platform
The evolution from traditional Computer System Validation (CSV) to Computer Software Assurance (CSA) reflects a shift towards more efficient, risk-based validation practices. A digital validation platform is instrumental in accelerating this transition and optimizing the entire system lifecycle.
Feature Traditional Computer System Validation (CSV) Modern Computer Software Assurance (CSA) Focus Documentation-heavy, comprehensive testing of all features Risk-based, critical thinking, testing focused on quality-critical functions Documentation Extensive, often redundant, paper-based Lean, targeted, digital, leveraging automated reports Testing Approach Manual, script-driven, exhaustive Automated, exploratory, leveraging vendor testing Efficiency Time-consuming, resource-intensive, slow Agile, efficient, faster time-to-market Regulatory Acceptance Established, but viewed as overly burdensome Growing acceptance, aligned with FDA’s current thinking Technology Use Limited automation, reliance on human effort High automation, AI-driven tools, continuous monitoring A digital validation platform enables the implementation of CSA by providing automated test scripts and tools for continuous validation. This means that instead of performing exhaustive, manual tests for every system change, the platform can automatically execute targeted tests on critical functionalities, providing immediate feedback on compliance status. This significantly reduces validation timelines from weeks or months to days or even hours, allowing for faster deployment of new software and updates.
Furthermore, these platforms facilitate paperless workflows, centralizing all validation documentation, test results, and audit trails in a secure, easily accessible digital format. This not only improves efficiency but also enhances audit readiness, as all necessary evidence can be quickly retrieved and presented during an FDA inspection. By streamlining the validation process and aligning it with CSA principles, a digital validation platform empowers organizations to maintain a continuously validated state, ensuring ongoing compliance without impeding innovation.
Frequently Asked Questions About FDA Electronic Signatures
Navigating the intricacies of 21 CFR Part 11 often raises specific questions. Here, we address some common inquiries regarding FDA electronic signature rules.
What makes an electronic signature legally equivalent to a handwritten signature under Part 11?
For an electronic signature to be considered legally equivalent to a handwritten signature under Part 11, several stringent requirements must be met, primarily outlined in § 11.100. Firstly, the organization must formally certify to the FDA, in writing, that electronic signatures used in their systems are intended to be the legal equivalent of handwritten signatures. This is typically done via a Letter of Non-Repudiation. Secondly, the electronic signature must be uniquely assigned to an individual, and the identity of that individual must be verified before the signature is established. Thirdly, the signature must incorporate multiple components for authentication (e.g., user ID and password) and be securely linked to the electronic record it signs. Finally, the signature’s manifestation must clearly display the signer’s printed name, the date and time of execution, and the meaning of the signature (e.g., approval, review, authorship). These combined elements ensure the integrity, authenticity, and non-repudiation of the electronic signature.
How do audit trail requirements differ between closed and open systems?
While both closed and open systems require secure, computer-generated, time-stamped audit trails that record all actions, the specific implementation and additional safeguards differ. For closed systems (§ 11.10), the audit trail must capture user attribution, date, time, and the nature of the action, providing a comprehensive, unalterable history within the controlled environment. For open systems (§ 11.30), all these requirements apply, but with the critical addition of encryption and digital signature standards. Because open systems transmit data over uncontrolled networks, the audit trail, along with the electronic record itself, must be protected by cryptographic methods to ensure its integrity and authenticity during transmission and storage. This means that open systems require more robust technical controls, such as independent record generation and verification against digital signature standards, to ensure the audit trail cannot be tampered with.
What is the role of Computer Software Assurance (CSA) in validating e-signature systems?
Computer Software Assurance (CSA) plays a transformative role in validating electronic signature systems by shifting the focus from extensive, documentation-heavy CSV to a more streamlined, risk-based approach. For e-signature systems, CSA means that validation efforts are concentrated on the critical-to-quality functions that directly impact the integrity and reliability of the electronic signature. Instead of exhaustively testing every feature, CSA emphasizes automated verification, leveraging vendor testing, and focusing on user acceptance testing for critical workflows. This approach ensures that the e-signature system performs its intended function accurately and reliably, while significantly reducing the burden of documentation and testing. CSA helps organizations achieve regulatory acceptance for their e-signature systems more efficiently by demonstrating that the system’s critical functions are fit for their intended use and comply with Part 11, without over-validating non-critical aspects.
Conclusion
The journey through FDA electronic signature rules, as defined by 21 CFR Part 11, underscores the critical importance of data integrity and authenticity in the life sciences. From its effective date in August 1997 to our current vantage point in October 2026, the core principles of Part 11 remain steadfast: electronic records and signatures must be as trustworthy and reliable as their paper counterparts. We’ve explored the foundational requirements, from dual-component authentication and secure record linking to the distinct controls for closed versus open systems, and the overarching influence of predicate rules.
The landscape of GxP compliance is continually evolving, driven by technological advancements and the need for greater efficiency. The shift away from traditional, manual validation methods towards modern, AI-driven solutions is not just a trend but a strategic imperative. By embracing digital validation platforms, organizations can overcome common compliance pitfalls, accelerate their system lifecycle, and ensure continuous audit readiness. These innovative solutions integrate robust technical controls—such as immutable audit trails, advanced encryption, and multi-factor access security—directly into their processes, strengthening the reliability of electronic signatures.
Achieving and maintaining FDA electronic signature compliance is about more than just checking boxes; it’s about fostering a culture of data integrity and ensuring the safety and efficacy of regulated products. With the right tools and a forward-thinking approach to compliance, organizations can confidently navigate the regulatory environment, streamline their operations, and build unwavering trust in their electronic data.